How to access HTTP proxy
At Mudfish, each mudfish nodes are enabled to support HTTP(S) proxy service. At this moment, Mudfish provides the following HTTP proxy service as follows:
-
HTTP proxy
This service uses plain HTTP protocol. So depending on your requests, some requests could be not encrypted.
- TCP Port 18080
-
HTTPS proxy
This service uses SSL connection to encrypt your HTTP requests. This service could be helpful to bypass the inspection of web traffics.
- TCP Port 18082
-
HTTP (sslbump) proxy
This service could be call as "Mudfish-in-the-middle". It performs decryption and encryption of CONNECT method and transparently redirects SSL traffic using Mudfish root certificate.
This method could be used to accelerate the gaming experience for example, Granblue Frantasy.
- TCP Port 18083
For SSL Bump, first install the Mudfish root CA certificate in your browser.
Web acceleration and caching
Mudfish's web acceleration uses a cache near the user to serve already-cached HTTP content without contacting the original server for every request. Unlike a CDN deployed by a website operator for its own content, this service applies to websites that the user visits and behaves more like a transparent proxy.
The service uses Cache-Terminator, a multithreaded, nonblocking cache server based on modified Varnish code. Together with Mudfish WAN optimization, it can help with slow overseas web access, video playback and downloads. It can also provide a proxy exit in another country. Websites see the node's public IP; the node may log the user's IP to prevent abuse.
Caching has a limitation: if an origin server updates content while a cached response is still valid under its Cache-Control headers, the node can serve older content. This may cause a page to display incorrectly. A user-facing cache-purge interface is not provided.
Get Public IPv4 address of mudfish nodes
You need to know the public IP or hostname if you want to set HTTP proxy service manually.
To get the public IP of hostname of mudfish nodes, you can visit the one of following links:
-
https://mudfish.net/api/staticnodes
JSON output. Each entry in the
staticnodesarray provides the public IPv4 address inipand the hostname inhostname. See Static node API response fields for the full field descriptions. -
https://mudfish.net/server/status
HTML output
For example
HTTP proxy is open publicly only with basic authentication based on Mudfish ID / password. An example is as follows:
-
Visits https://mudfish.net/server/status and checks 'US East (Miami - QudraNet)' name. Its public IP is 155.94.209.102.
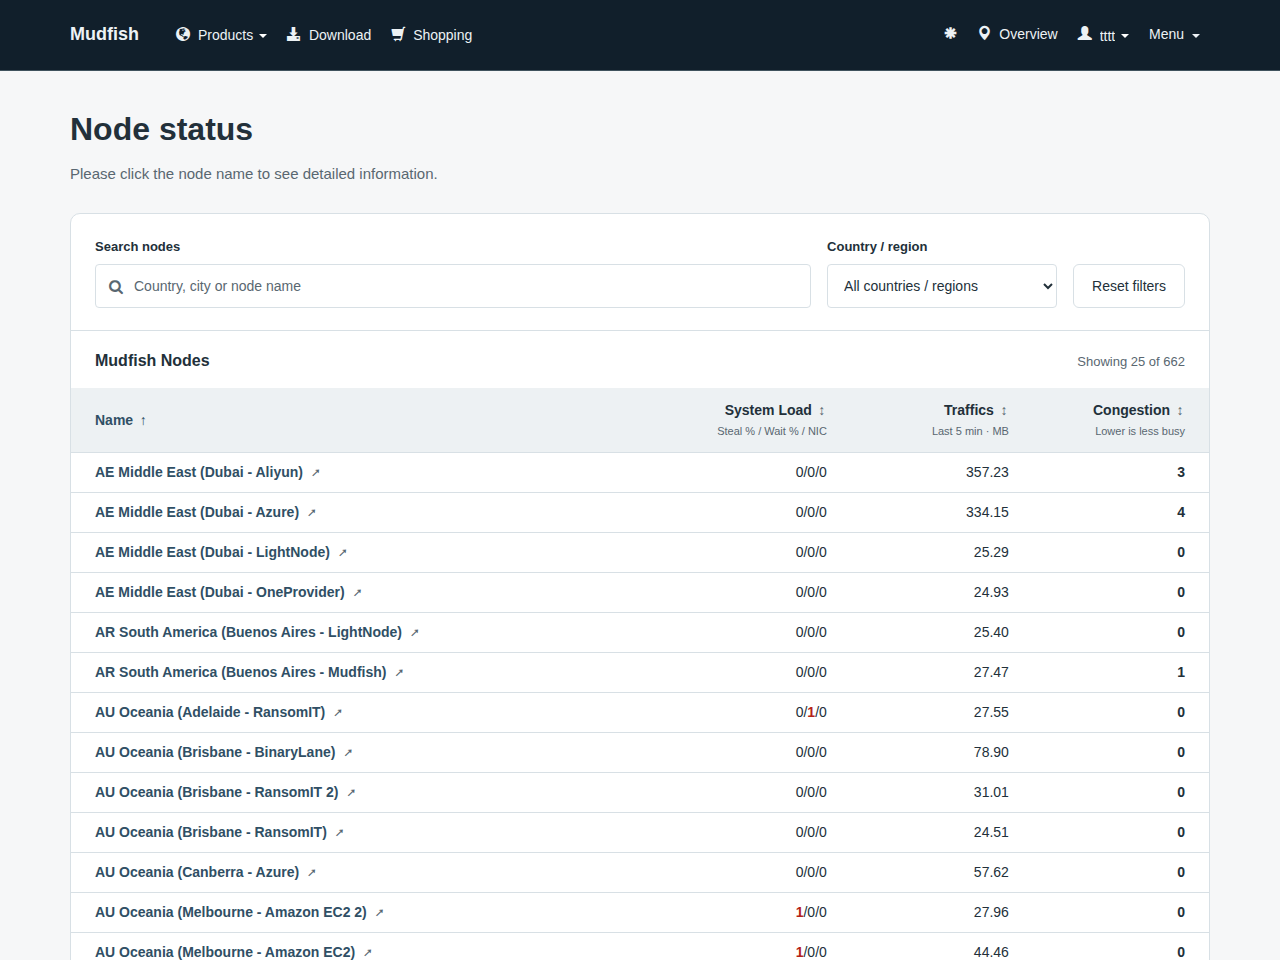
-
So you can set HTTP proxy setting with accessing IPv4 155.94.209.102 and TCP 18080 port.
If you want to use other HTTP proxy service, you can use TCP 18082 or TCP 18083 ports.
If you're not familiar with changing the proxy setting for your browser, please check Google Chrome Proxy Settings link for Chrome.
Google Chrome
In the older Chrome interface illustrated here, open the menu, choose “Settings”, expand “Advanced”, then select “Open proxy settings”. On Windows, this opens the system proxy settings also used by Internet Explorer.


Firefox
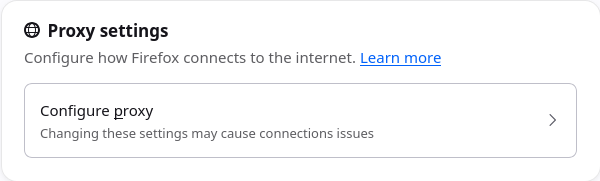
Open about:preferences, search the settings for proxy, and open the proxy configuration dialog. Select
“Manual proxy configuration”, then enter the appropriate proxy address and
port. Confirm the changes to return to Firefox.
Internet Explorer
In Internet Explorer 7 and later, open “Tools → Internet Options → Connections → LAN settings”. Enable “Use a proxy server for your LAN” and “Bypass proxy server for local addresses”. In “Advanced”, enter the address and port in the HTTP field, then confirm the dialogs.

Internal-address HTTP and SOCKS proxies
The public-address services above use Mudfish ID/password authentication and ports 18080, 18082 or 18083. Older internal-address examples use different ports and require Mudfish to be running so that the internal network is reachable.
For example, the documented internal address of the Korea KT node is
10.255.96.1:
| Internal service | Address | Port |
|---|---|---|
| HTTP | 10.255.96.1 | 8080 |
| SOCKS | 10.255.96.1 | 8081 |
Use the node's actual internal address when selecting a different node. For public access, use its public address and the public service's port instead.
Configure internal HTTP access
Use the browser steps above with 10.255.96.1 and port 8080 in the HTTP proxy
field. In Firefox, use “Manual proxy configuration”. In the Windows Internet
Options dialog, use the HTTP row under “LAN settings → Advanced”.
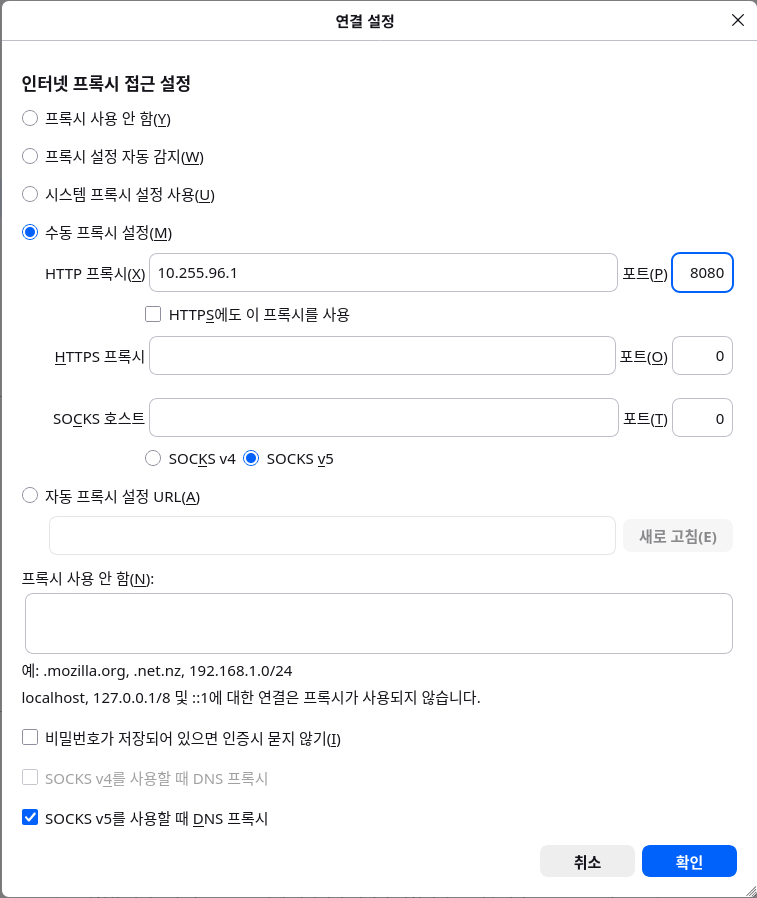
This screenshot is in Korean: “수동 프록시 설정” means “Manual proxy configuration”, “HTTP 프록시” means “HTTP Proxy”, and “포트” means “Port”. It shows the internal address and port from the example above.
Configure internal SOCKS access without WPAD
You can configure SOCKS directly if WPAD is unavailable:
- Firefox: open
about:preferences, search forproxy, open the proxy configuration dialog, select manual proxy configuration, and enter10.255.96.1with port8081in the SOCKS Host fields. - Internet Explorer: open “Internet Options → Connections → LAN settings”,
enable the proxy and local-address bypass, then open “Advanced”. Enter
10.255.96.1and8081in the Socks row. - Chrome on Windows: open the system proxy settings as described above, then follow the Internet Explorer procedure from the Connections tab.
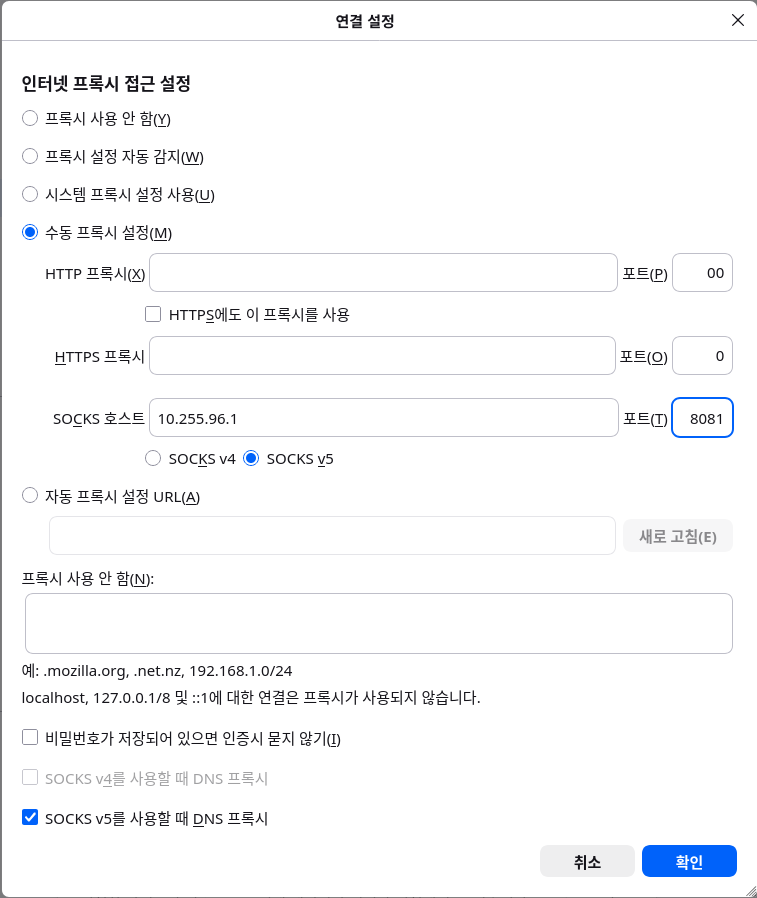
This screenshot is in Korean: “SOCKS 호스트” means “SOCKS Host” and “포트” means “Port”. Select SOCKS v5. The checked option “SOCKS v5를 사용할 때 DNS 프록시” means “Proxy DNS when using SOCKS v5”.
Save all dialogs. These manual settings route the browser's traffic through the configured proxy. When you stop Mudfish, disable the internal proxy settings too; otherwise, browsing may stop working.
Report documentation errors or suggestions on the Mudfish forums.